
At a glance
- Black-box AI penetration testing tests the system from an external attacker's perspective with minimal or no internal knowledge, while white-box AI penetration testing gives the tester broad internal access to examine code, architecture, model configuration, and supporting infrastructure. Black-box offers higher attacker realism but may miss deep internal flaws; white-box offers deeper coverage but does not realistically reproduce a purely external attack. The right choice depends on whether the priority is external resilience, internal coverage, or both.
- Use black-box testing for public-facing AI APIs, chatbots, or assessments focused on external attacker behavior.
- Use white-box testing for pre-deployment reviews or high-risk systems where code, architecture, model configuration, and supply-chain weaknesses require inspection.
- Use gray-box or combined testing when both realistic external behavior and deeper internal coverage are required.
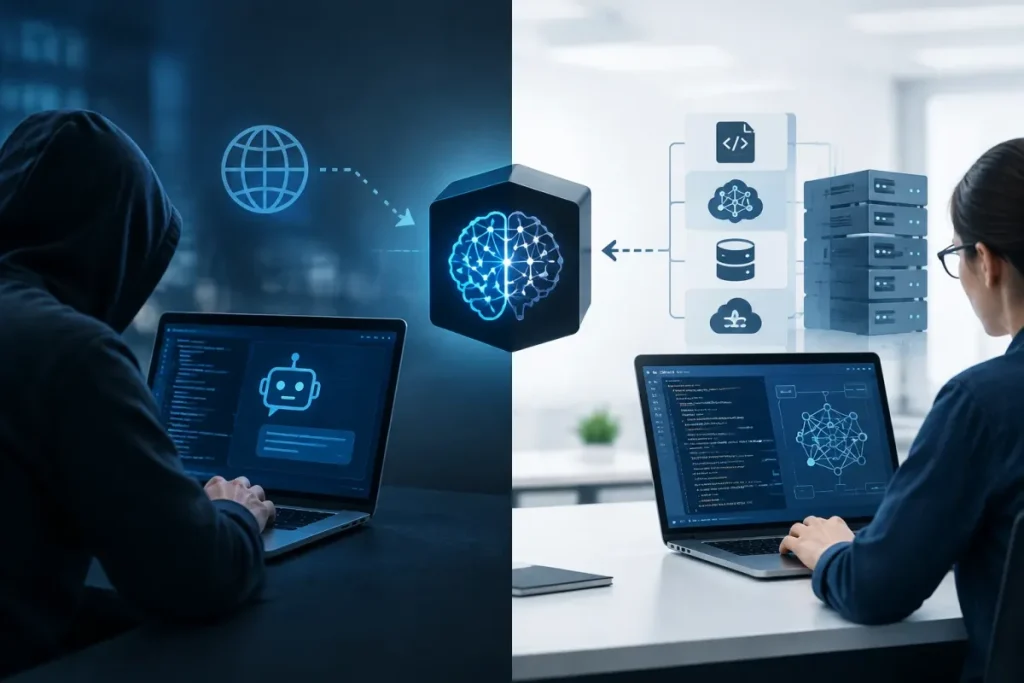
Black-box AI penetration testing tests an AI system from an external attacker’s perspective with minimal or no internal knowledge. White-box AI penetration testing gives testers broad access to examine code, architecture, model configuration, and supporting infrastructure. Black-box provides greater realism; white-box provides deeper coverage. The right choice depends on the assessment objective.
A gray-box or combined assessment can address both priorities when partial internal access is realistic or when external resilience and internal coverage are both required.
At a glance: black-box vs. white-box AI testing
| Dimension | Black-box AI testing | White-box AI testing |
|---|---|---|
| Access and knowledge | Minimal or no internal knowledge; the tester uses the information and access authorized for the engagement. | Broad internal visibility into code, architecture, configurations, documentation, model configuration, or related implementation details. |
| Threat model | External attacker or unprivileged user. | Privileged review of internal implementation and architecture. |
| Attacker realism | Generally higher because the tester starts with little or no internal context. | Lower for a purely external-attacker simulation because the tester has privileged information. |
| Technical coverage | Limited by what can be observed or reached externally and may miss hidden internal flaws. | Generally broader and deeper across implementation, configuration, and architecture. |
| Best-fit objective | Evaluate external resilience and exposed attack paths. | Examine internal implementation, configuration, and architectural weaknesses. |
| Best use cases | Public-facing AI APIs, chatbots, and exposed AI-enabled applications. | Pre-deployment reviews and high-risk systems requiring internal inspection. |
Neither method is universally superior. Black-box testing answers how the exposed system responds to an external threat, while white-box testing answers deeper questions about how the system is built and configured.
What black-box AI penetration testing means
Access and threat model
Black-box AI penetration testing begins with minimal or no knowledge of the system’s internal workings. The tester approaches the authorized assessment as an external attacker or unprivileged user, using publicly available information and only the information explicitly provided for the engagement. Before setting access conditions, review our AI threat modeling guide to map the system’s assets, trust boundaries, and attack paths.
For an AI system, the exposed scope might include model behavior, an application wrapper, a public-facing API, a chatbot, or another external interface. These surfaces are not automatically included in every assessment. The organization must define what is reachable, what access is allowed, and which components are in scope.
Strengths and limitations
The main strength of a black-box assessment is external-attacker realism. It shows how the system appears and responds to someone without source code, architecture documentation, privileged credentials, or other internal context.
That restricted perspective also creates blind spots. Black-box testing may miss weaknesses that require authentication, source-code visibility, internal architecture knowledge, or access to implementation details. It is valuable for assessing external resilience, but it does not provide complete visibility into internal security.
What white-box AI penetration testing means
Internal visibility and assessment focus
White-box AI penetration testing gives testers broad internal access to relevant information. Depending on the authorized scope, this may include source code, architecture, configurations, documentation, model configuration, and related implementation details.
This visibility allows the assessment to examine how the AI-enabled system is built and connected, rather than only how it behaves from the outside. Depending on the engagement, the review may include code, configuration, data flow, paths through the application, and authorized dynamic testing.
Strengths and limitations
The main advantage of a white-box assessment is internal depth. It can reveal implementation and configuration flaws that black-box testing may not observe, making it useful for pre-deployment reviews and high-risk systems that require detailed technical inspection.
White-box testing does not realistically reproduce a purely external attacker who starts with no internal knowledge. Its privileged view is designed for broader technical coverage, not for an uninformed-attacker simulation.
What each approach can reveal in an AI system
Black-box: exposed behavior and attack paths
Use black-box AI testing when the priority is understanding external attacker behavior. This is a natural fit for an authorized review of a public-facing AI API, chatbot, or other exposed AI-enabled application.
The assessment can examine what an external or unprivileged user can discover, reach, and observe under the agreed conditions. It can also identify exposed interfaces and behaviors that require security attention without relying on source-code or architecture access.
Its limitation is fundamental: an external assessment may not identify weaknesses hidden behind authentication or dependent on internal code, configuration, data flow, or architecture.
White-box: implementation and configuration depth
Use white-box AI testing when the priority is internal coverage. It can support a pre-deployment review or an assessment of a high-risk system where the organization needs visibility into code, architecture, configuration, and related implementation details. For the distinction between these engagement types, read AI security assessment vs AI penetration test.
White-box testing can examine weaknesses that are not observable from the outside and connect relevant components within the assessed architecture. However, findings must be interpreted in the context of privileged access: they do not automatically describe what an uninformed external attacker could discover.
AI assessment scope and access levels
AI penetration testing can cover different combinations of models, applications, interfaces, and infrastructure. Before selecting a method, define the system and access conditions rather than assuming that every AI component is included. For a structured way to evaluate risk before defining the engagement, see the AI security risk assessment guide.
- Black-box scope: externally reachable behavior, public-facing APIs, chatbots, and exposed application interfaces, with minimal or no internal information.
- Gray-box scope: partial knowledge, authenticated access, or limited internal context that reflects a realistic user or operational role.
- White-box scope: broad access to code, architecture, configuration, documentation, and other implementation details authorized for review.
For each engagement, clarify whether the scope includes model behavior, application wrappers, APIs, data pipelines, supporting infrastructure, or other connected components. Confirm the application state—such as development, staging, pre-deployment, or production—and the access the tester will receive.
Model interfaces, prompts, system instructions, training data, retrieval systems, agents, model weights, and pipelines should be treated as engagement-specific scope questions. Their inclusion, access model, and assessment procedures must be confirmed for the individual system rather than assumed to be standard for every AI assessment.
A practical AI penetration-testing workflow
A defensively scoped assessment can follow a common structure while changing the available information and depth of review:
- Define the objective and threat model. Decide whether the assessment represents an external attacker, an authenticated user, an internal reviewer, or more than one perspective.
- Confirm scope and access. Document the AI components, interfaces, infrastructure, credentials, documentation, and implementation materials included in the engagement.
- Assess the authorized attack surface. For black-box testing, focus on externally observable behavior and reachable interfaces. For white-box testing, add code, configuration, architecture, and related internal analysis where authorized.
- Validate findings. Confirm that each reported weakness is relevant to the agreed system, access level, and threat model.
- Report by perspective. Separate externally observable findings from issues discovered only through privileged internal visibility.
Select procedures, tools, metrics, and reporting fields according to the system and engagement. For guidance on measuring results and reporting risk, see the AI security metrics and KPIs guide.
When to choose black-box, white-box, or gray-box testing
Choose black-box for external attacker realism
Use black-box AI penetration testing when the main question concerns external resilience. It is well suited to an authorized review of a public-facing AI API, chatbot, or exposed AI-enabled application from outside the trust boundary.
Choose white-box for internal coverage
Use white-box AI penetration testing for pre-deployment reviews or high-risk systems where code, architecture, model configuration, and supply-chain weaknesses require inspection. Confirm which supporting components are actually in scope rather than assuming that specialized assets or pipelines are included.
Choose gray-box or combined testing for both
Gray-box AI penetration testing uses partial knowledge, authenticated access, or limited internal context. It is useful when that level of access reflects the realistic threat or when the organization needs more coverage than a purely external test provides without granting full internal visibility. To consider when testing is warranted, see when an AI application needs a penetration test.
A combined assessment can use black-box testing for the external perspective and white-box testing to investigate implementation or configuration issues that external testing cannot establish. This preserves the distinction between external realism and internal technical coverage.
The decision should reflect the security objective, threat model, scope, application state, and desired assurance. No single method is the best choice for every AI system.
Frequently asked questions
What is the difference between black-box and white-box AI penetration testing?
Black-box AI penetration testing uses minimal or no internal knowledge and models an external attacker. White-box AI penetration testing gives testers broad internal visibility into code, architecture, configurations, model configuration, and related implementation details. Black-box emphasizes external realism; white-box emphasizes internal depth.
Which method better simulates a real external attacker?
Black-box testing generally provides greater external-attacker realism because the tester starts with little or no internal knowledge. White-box testing is not an equivalent simulation of a purely external attacker because testers receive privileged information.
Which method provides broader internal coverage?
White-box testing generally provides broader and deeper internal coverage. Its access can reveal implementation and configuration flaws that black-box testing may not observe, although no method guarantees that every weakness will be found.
Should an organization combine black-box and white-box assessments?
Combine them when both external resilience and internal coverage are important. Black-box testing supplies the external perspective, while white-box testing can investigate issues that require implementation or configuration visibility. A gray-box assessment may be sufficient when partial access reflects the realistic threat.
Conclusion: match the method to the security question
Black-box AI penetration testing is the stronger fit for external-attacker realism. White-box AI penetration testing is the stronger fit for internal implementation and configuration depth, but it does not reproduce an uninformed external attacker. Gray-box or combined testing can address both priorities.
Select the method based on the security question, threat model, scope, application state, and desired assurance—not on the assumption that one approach is always best.