
ABAC for AI agents: key takeaways
- For AI agents, attribute-based access control (ABAC) makes authorization decisions dynamically at request time by evaluating attributes of the agent and its delegation, the requested action, the target tool or data, and the surrounding context. This enables fine-grained, least-privilege control for changing agent tasks; in practice, ABAC is often layered over RBAC rather than treated as a universal replacement.
- Evaluate each agent request against attributes for the agent, delegating user, action, resource, and context.
- Use explicit agent identity and delegation scope or expiration metadata.
- Apply policy decision and enforcement points to tools, APIs, and data access.
- Use ABAC as a fine-grained layer over a baseline RBAC model where appropriate.
For AI agents, ABAC makes authorization decisions dynamically at request time by evaluating attributes of the agent, delegation, action, target tool or data, and context. This enables fine-grained, least-privilege control for changing tasks; ABAC is often layered over RBAC rather than replacing it.
What is ABAC for AI agents?
Attribute-Based Access Control (ABAC) authorizes an AI agent by evaluating the attributes of each access request instead of relying only on a preassigned role. The policy considers who or what is making the request, which resource or tool is involved, what operation is requested, and the surrounding circumstances.
Authorization is evaluated when an agent calls a tool, accesses data, or performs an operation. The result can change when the task, resource, requested operation, tenant, time, delegation scope, or environment changes.
ABAC versus static role-only authorization
RBAC grants permissions through roles and provides a useful baseline. However, changing agent tasks can require many narrowly defined role combinations. ABAC evaluates conditions for each request instead.
That does not make ABAC universally better than RBAC. A practical architecture often uses RBAC for broad boundaries and ABAC for contextual, task-level, and operation-level restrictions.
The four attribute groups used in agent authorization
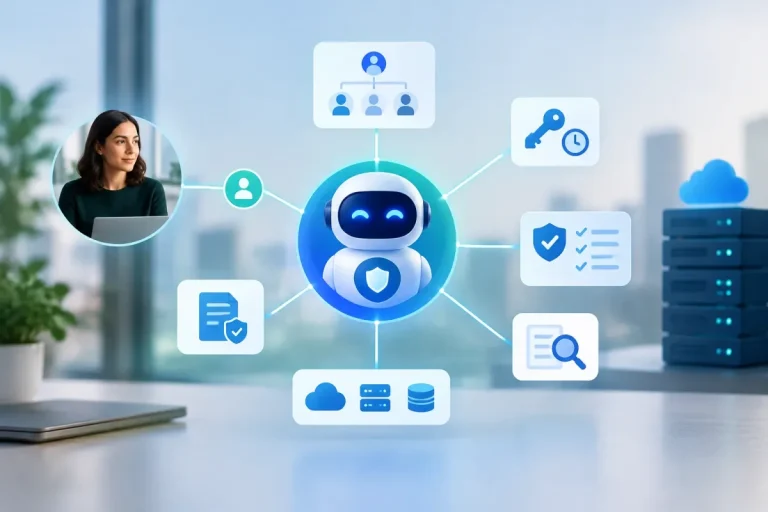
ABAC policies typically organize request inputs into four groups. Delegation and relationship information commonly accompany subject evaluation because an agent may act on behalf of a human.
| Attribute group | What it describes | Authorization role |
|---|---|---|
| Subject or agent | The agent identity, delegating human, authority, and delegation scope | Establishes who is acting and under whose authority |
| Resource | The target tool, API, application, dataset, record, tenant, ownership, or sensitivity classification | Defines what the agent is trying to access |
| Action or operation | The requested operation, such as reading, downloading, forwarding, or modifying | Limits what the agent may do with the resource |
| Environment or context | The current task, time, tenant, and other relevant conditions | Determines whether the request is valid in its circumstances |
Subject and agent attributes
The subject is not simply “the AI.” The policy should identify the particular AI agent and preserve the identity of the human delegator when the agent acts on that person’s behalf. It can also evaluate the authority and scope attached to the delegation. For a deeper comparison of the two identity types, see Human Identity vs. AI Agent Identity.
An agent’s identity alone does not determine authorization. The agent must also operate within the applicable delegation, task, and policy boundaries.
Resource attributes
Resource attributes describe the target: a tool, API, application, dataset, record, or other protected object. Tenant, ownership, authorized scope, and sensitivity classifications can distinguish resources that should not receive the same treatment.
Action and context attributes
The policy should evaluate what the agent wants to do, not only what it wants to access. Reading a record is different from downloading or forwarding it. Context such as the current task, tenant, time, and environment allows the policy to make a request-specific decision rather than grant a broad permission that applies in every circumstance.
How an ABAC authorization decision works
Authentication, delegation, and authorization
Authentication establishes an identity. Delegation describes when an agent acts for a human or another authority. Authorization decides whether that identified agent may perform the requested operation on the target resource. These are related but distinct steps.
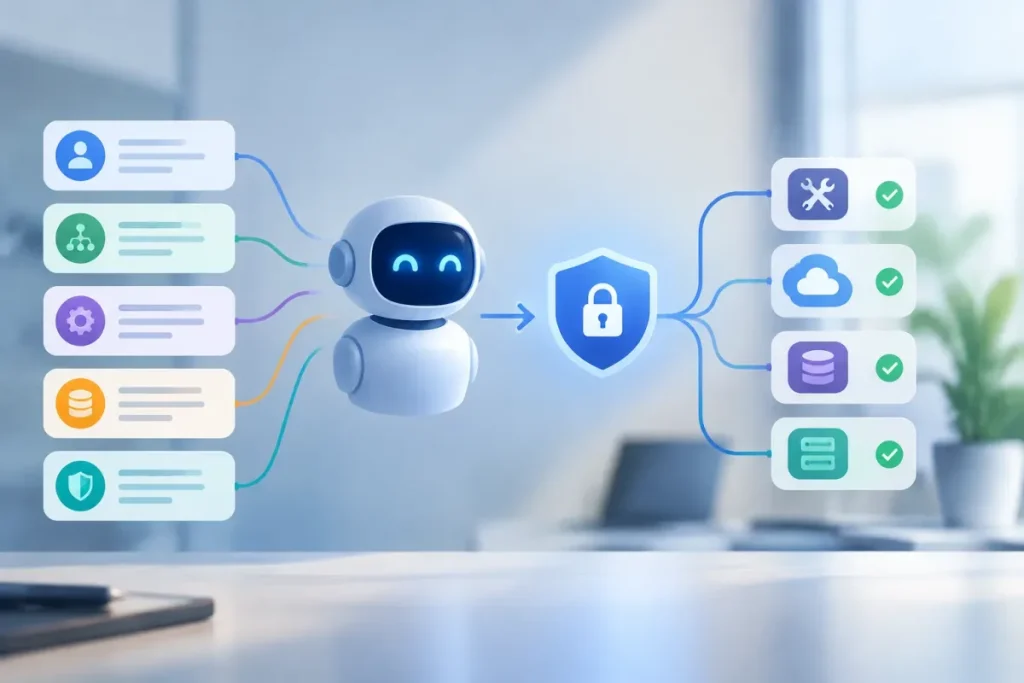
A typical request flow is:
- The agent presents its distinct identity to the protected tool, API, application, or data service.
- The request carries delegation context, including the delegating human and applicable scope.
- The authorization layer gathers subject, resource, action, and environment attributes.
- A Policy Decision Point (PDP) evaluates those inputs against policy.
- A Policy Enforcement Point (PEP) allows or denies the request at the protected boundary.
The policy should evaluate the agent, delegating user, requested action, target resource, task, and relevant context for every request. This ties authorization to the actual operation rather than to the agent’s identity alone.
The PDP produces the decision; the PEP applies it where access occurs. A PEP can sit at a tool, API, application, or data boundary. The language model may propose an action, but the enforcement point must independently determine whether that action is permitted.
A concrete AI-agent ABAC example
Allow reading, but deny downloading or forwarding
Consider an agent assigned a defined task involving sensitive records. A policy could evaluate:
- the distinct agent identity;
- the delegating user and that user’s authority;
- the defined task and delegation scope;
- the target records, tenant, and authorized resource scope;
- the requested operation; and
- the relevant time and environmental context.
If those attributes satisfy policy, the agent may read the sensitive records needed for the defined task. The same policy can deny an attempt to download or forward them, or to access records outside the authorized scope.
This example shows why access to a resource and permission to perform every operation on that resource are separate decisions. It is a policy pattern, not complete production policy syntax.
ABAC versus RBAC for agentic AI
| Consideration | RBAC | ABAC |
|---|---|---|
| Decision inputs | Permissions associated with a role | Attributes of the subject, resource, action, and context |
| Timing | Often based on an assigned role boundary | Evaluated at request time |
| Granularity | Useful for broad, stable access boundaries | Useful for contextual, task-level, and operation-level restrictions |
| Changing combinations | May require additional narrowly scoped roles | Can express varying conditions through policy attributes |
| Practical use | Often serves as a baseline | Often adds fine-grained conditions to that baseline |
RBAC answers which permissions are associated with a role. ABAC adds request-specific questions: which agent is acting, for which delegator, against which resource, for which task, using which operation, and under what conditions?
For agents whose tasks change, expressing every combination as a separate role can create role-management complexity. A hybrid model keeps RBAC as a broad boundary while ABAC narrows access at runtime—for example, by restricting the tenant, task, record scope, operation, or time.
ABAC is not an automatic replacement for RBAC. The appropriate design depends on the authorization boundaries and operational requirements of the environment.
Agent identity and delegated authorization
Each AI agent should have a distinct identity, credentials, policies, and ownership rather than relying on a human credential or shared service account. Dedicated identities make it easier to separate actions, apply least privilege, review activity, and revoke access. For broader identity and access governance, see IAM for AI applications.
A distinct identity gives the authorization layer a subject to evaluate, but it does not grant permission by itself. The resource, operation, task, delegation, and context must still satisfy policy.
When an agent acts on behalf of a person, authorization should account for both parties. The agent may be technically capable of calling a tool while the delegating human’s authority or delegation scope does not cover the requested action. For related risks from unsafe tool use, see AI agent tool misuse.
Delegation context should remain available throughout the agent’s operation. Otherwise, a later tool call or multi-step action may be evaluated without the relationship and scope that justified the original request.
Least-privilege control for tools, data, and operations
Least privilege means giving the agent only the access needed for the current task and operation. ABAC can apply that principle across:
- Task: restrict access to the work the agent is performing.
- Resource: limit access to approved tools, records, datasets, or tenants.
- Operation: distinguish reading from downloading, forwarding, modifying, or other actions.
- Scope: prevent access outside the authorized organizational or data boundary.
- Time and environment: apply relevant conditions to when and under what circumstances the request is made.
These checks should occur outside the language model. A model-generated plan or tool call is an input to authorization, not an authorization decision.
Implementation checklist
- Give every agent a distinct identity, credentials, ownership, and policy boundary.
- Evaluate the agent, delegating human, delegation scope, resource, action, task, and relevant context for each request.
- Place PDP and PEP controls at tool, API, application, and data boundaries as appropriate.
- Keep authorization checks outside the language model.
- Verify the origin, validity, freshness, and propagation of attributes across multi-step workflows.
- Log authorization requests, decisions, and relevant agent operations.
- Review whether policies still match actual tasks and access needs, and provide revocation controls.
- Define how missing or conflicting attributes are handled and how policy-service unavailability affects requests.
Request-time authorization also introduces operational questions around policy-evaluation latency, attribute retrieval, throughput, cost, and multi-step workloads. These details are environment-specific and should be tested rather than inferred from the ABAC model itself. For a broader implementation checklist, see AI security controls.
What ABAC does not solve by itself
ABAC is an authorization layer. It can decide whether an agent may perform a requested operation under specified conditions, but it does not solve every AI-agent risk. It should not be presented as automatic protection from prompt injection, universal security, or regulatory compliance.
It also does not eliminate the need for identity management, trustworthy attributes, monitoring, lifecycle controls, or appropriate human approval. The central model remains: evaluate the agent and delegation, resource, action, and context at request time; enforce the decision outside the language model; and apply the narrowest permission needed for the task.