
Key takeaways
- Human identity and AI agent identity are different IAM identity classes: a human identity belongs to a person who originates intent and is directly accountable, while an AI agent identity belongs to a distinct non-human software actor that executes delegated goals and needs separately scoped, attributable credentials and governance. The agent's identity should be linked to—not substituted for—the human or system that authorized it.
- Use a distinct, verifiable identity for each agent or agent instance where appropriate.
- Apply scoped, task-specific, short-lived or revocable credentials rather than sharing human credentials.
- Record both who authorized the work and which agent executed it.
- Enforce least privilege, bounded delegation, approval/HITL controls where risk warrants, and monitoring of instructions, tool calls, and downstream actions.
Human identity and AI agent identity are different IAM identity classes: a human identity belongs to a directly accountable person, while an AI agent identity belongs to a distinct non-human software actor executing delegated goals. Link the agent to—not substitute it for—the authorizing human or system.
Human identity vs. AI agent identity
Key takeaways
- Human identity represents a person who originates or directly approves intent; AI agent identity represents a distinct non-human software actor that executes delegated goals.
- Use a distinct, verifiable identity for each agent or agent instance where appropriate, rather than sharing human credentials.
- Use scoped, task-specific, short-lived or revocable credentials and apply least privilege, bounded delegation, and approval controls where risk warrants them.
- Record both who authorized the work and which agent executed it, including relevant tools, resources, and delegation handoffs.
What a human identity represents
A human identity represents a person who originates, authorizes, or directly participates in an action. Accountability is tied to that person. IAM access is typically managed through individual authentication, assigned roles or attributes, and a lifecycle connected to the person’s organizational relationship.
Human identity processes commonly cover onboarding, access changes, removal, and periodic entitlement review. The person authenticates directly, although a person may also authorize delegated work performed by software.
What an AI agent identity represents
An AI agent identity represents a distinct, verifiable non-human identity for software that operates autonomously or semi-autonomously toward a goal. The agent can interpret instructions, select tools, make runtime decisions, and adapt how it performs delegated work.
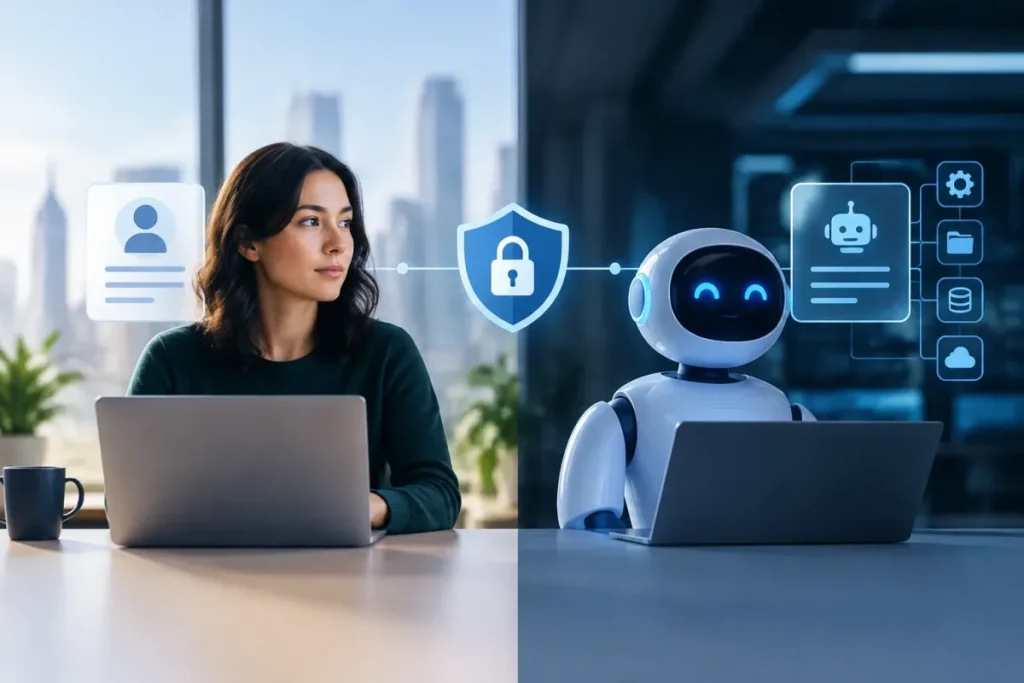
The agent is not the human identity and does not replace or inherit it. The authorizing human or system and the executing agent should remain separate but linked identities, with separate policies and an auditable delegation relationship.
Three identity categories
| Category | What it represents | Key governance concern |
|---|---|---|
| Human identity | A person who provides or approves intent directly | Individual authentication, accountability, and organizational lifecycle |
| Deterministic workload identity | A service, workload, or automated process performing defined functions | Deployment ownership, machine credentials, and workload access |
| AI agent identity | A non-human software actor that pursues delegated goals and can make runtime decisions | Delegation, autonomy, task scope, behavioral monitoring, and attributable execution |
AI agent identities are generally a category of non-human identity, but non-human identity is broader than AI agents. A service account, API key, workload identity, or machine credential is not automatically a complete agent identity. An agent may use one of these credentials, but the credential alone does not identify the agent’s owner, delegated authority, behavior, or decision context. For the broader IAM framework behind these identity categories, see IAM for AI Agents: A Complete Guide.
Side-by-side comparison
| Dimension | Human identity | AI agent identity |
|---|---|---|
| Actor | A biological person | A distinct non-human software actor |
| Intent | Originates or is directly approved by the person | Delegated by a human or system and interpreted toward a goal |
| Autonomy | The person makes or approves decisions | The agent can select tools, make runtime decisions, and adapt execution |
| Predictability | Access is associated with the person and assigned permissions | Behavior is more dynamic and less predictable than a traditional workload |
| Authentication | Usually interactive individual authentication | Programmatic authentication using cryptographic or workload-style credentials |
| Credentials | Individual user credentials | Distinct, attributable credentials or a linked workload credential; never shared human credentials |
| Authorization | Roles, attributes, or permissions assigned to the person | Narrow, task-specific, and time-bound where possible, evaluated against runtime context |
| Delegation | May authorize or approve an action | Executes delegated authority without automatically receiving the sponsor’s full access |
| Lifecycle | Onboarding, access changes, review, and removal tied to the person | Issuance, deployment, ownership, rotation, expiry, decommissioning, and rapid revocation |
| Audit trail | Records the person and the action | Records the sponsor, agent or instance, credentials, tools, resources, actions, and delegation chain |
Intent, autonomy, and behavior
A human generally supplies or approves intent directly. An AI agent receives a goal or delegated authority and determines how to pursue it within its permissions and runtime context.
While executing a task, the agent may choose a tool, call an API, access a resource, or hand work to another agent. The human or system remains the source of authorization where applicable, but the agent is the software actor performing the operation.
Static human-style IAM assumptions are insufficient because an agent can interpret goals and adapt its behavior. Governance therefore needs both access controls and behavioral monitoring, including visibility into instructions, tool calls, downstream actions, and relevant runtime context. For a broader governance framework, see AI agent governance guide.
Delegated authority and agent identity
User-directed tasks
When an agent performs work at a user’s request, use narrowly scoped delegated authority linked to the invoking human. Limit the delegation to the resources and operations required for that task. The agent must not automatically receive the user’s complete access.
Autonomous system-to-system work
For autonomous system-to-system work, use a dedicated AI agent identity appropriate to the defined function. Restrict its permissions to that function and preserve the sponsoring system and agent execution context separately.
Combined workflows and handoffs
When a workflow includes human approval and agent execution, preserve both contexts. Record who authorized or approved the work and which agent or agent instance executed it. Across tools, external systems, trust boundaries, or subagent handoffs, carry forward the sponsor, executing agent, credentials, delegation scope, and relevant approval context.
Authentication, authorization, and runtime policy
Use distinct, attributable credentials
Agents should authenticate programmatically with cryptographic or workload-style credentials rather than ordinary user passwords. Use a distinct, verifiable identity for each agent or agent instance where appropriate, and never share human credentials with an agent.
Credentials and permissions should be task-specific, narrowly scoped, short-lived or time-bound where possible, and capable of rotation, expiry, and rapid revocation. The agent identity, credential, owner, sponsor, and permitted function should remain discoverable. For a focused treatment of expiring agent credentials, see short-lived tokens for AI agents.
Apply least privilege and bounded delegation
Authorization should consider the requested action, tool, resource, data, represented user, execution context, delegation scope, and credential validity. A user’s ability to perform an operation does not automatically mean the agent should receive the user’s full permissions.
Add runtime restrictions and approvals
Restrict the tools, resources, data, and operations the agent can reach. Use approval or human-in-the-loop controls where risk warrants them, especially for actions with significant impact or difficult reversal. Monitor whether the agent uses its tools and permissions within the intended scope.
Lifecycle, ownership, and revocation
Human identities are generally managed through individual identity and organizational lifecycle processes. AI agent identities are managed through deployment, runtime ownership, sponsorship, and operational revocation processes.
Human identity access usually persists while the person’s organizational relationship and entitlements remain valid. Agent access should be more closely tied to its deployment, task, owner, and purpose; short-lived or task-bound credentials can reduce persistent access where the architecture supports them. Traditional workload credentials may persist for the life of a service, so they require particular attention when used by an agent. For a structured lifecycle assessment, see AI agent risk assessment lifecycle.
Governance should cover:
- Discovery and identity issuance
- Named ownership and sponsorship
- Access review and permission changes
- Credential rotation, expiry, and renewal
- Deployment changes and decommissioning
- Rapid revocation during suspected misuse or compromise
- Succession and break-glass planning when an owner or dependency changes
Long-lived or orphaned credentials are especially risky because an agent may continue operating after its purpose, owner, or deployment context has changed.
Auditability and accountability
A useful audit record preserves the complete identity relationship, not only the credential that reached a resource. At minimum, link:
- The human or system that authorized or approved the work
- The executing agent or agent instance
- Any subagents or delegation handoffs
- The credentials used
- The tools and resources accessed
- The actions taken and relevant runtime context
This dual-identity model answers two separate questions: who authorized the activity, and which software actor performed it? The relationship should remain intact across tool calls, system boundaries, and agent handoffs so that execution identity is not lost when authority is delegated.
Common risks and controls
| Risk | Useful control |
|---|---|
| Shared or inherited human credentials | Use distinct agent identities and scoped delegated authority |
| Overprivileged agent access | Apply least privilege, task scope, and bounded delegation |
| Persistent or orphaned credentials | Assign owners, enforce expiry and rotation, and support rapid revocation |
| Autonomous overreach or tool misuse | Restrict tools and resources, monitor behavior, and require approval where risk warrants it |
| Unclear responsibility | Record the sponsor, agent, owner, and delegation lineage |
| Fragmented audit trails | Link credentials, tools, resources, actions, agents, subagents, and authorizing identities |
Practical governance workflow
- Identify the actor: determine whether the activity belongs to a person, deterministic workload, or autonomous AI agent.
- Assign ownership: record the responsible human or system sponsor and the agent’s defined function.
- Issue a distinct identity: create a verifiable agent or agent-instance identity where appropriate.
- Scope authority: define the tools, resources, data, operations, and represented user available to the agent.
- Authenticate programmatically: use attributable workload-style or cryptographic credentials, not shared human passwords.
- Evaluate at runtime: enforce task scope, delegation limits, credential validity, and approval requirements.
- Record execution: preserve the authorizing identity, executing agent, credentials, tools, resources, actions, and handoffs.
- Review and revoke: rotate, expire, review, decommission, or rapidly revoke the identity as its ownership or purpose changes.
Conclusion
A human identity represents the person who originates or authorizes intent; an AI agent identity represents the distinct software actor that executes delegated work. Treating them as separate IAM identities enables least-privilege access, bounded delegation, clearer accountability, and a complete audit trail. The agent identity should remain linked to—not substituted for—the authorizing human or system.
For enterprise IAM, security architecture, delegation, lifecycle governance, and accountability, validate specific protocols, identity schemas, credential formats, runtime policy engines, compliance controls, and approval thresholds against the organization’s threat model, architecture, regulatory obligations, and security review process.