
MCP HTTP security essentials
- MCP exposed over HTTP should be treated as a high-risk trust boundary: secure it with HTTPS, strong and short-lived authentication, least-privilege authorization, strict validation, isolation, approval gates for dangerous actions, and centralized logging and monitoring.
- Enforce HTTPS and protect the endpoint behind an authenticated gateway or equivalent access-control layer.
- Use standards-based authentication and authorization appropriate to the deployment; prefer short-lived, narrowly scoped credentials and validate tokens, redirect URIs, and sessions.
- Apply least privilege with explicit per-tool, per-user, and per-agent permissions; separate read-only from write or administrative operations.
- Validate tool arguments, schemas, content, and outputs; treat external context as untrusted and design defenses against prompt or context injection.
MCP exposed over HTTP should be treated as a high-risk trust boundary: secure it with HTTPS, strong and short-lived authentication, least-privilege authorization, strict validation, isolation, approval gates for dangerous actions, and centralized logging and monitoring.
Model Context Protocol (MCP) connects AI applications with external data sources, services, and tools. A host coordinates the application, clients communicate with MCP servers, and servers expose tools or data. Because these workflows can influence external systems, HTTP exposure is not safe by default. Security must cover the transport and the broader host-client-server architecture.
MCP HTTP security essentials
| Risk | What can go wrong | Primary controls |
|---|---|---|
| Endpoint exposure | Unauthorized access, token theft, session hijacking, or impersonation. | HTTPS/TLS, authenticated gateways, private networking, and segmentation. |
| Identity and sessions | Weak validation, static credentials, or persistent sessions expose connected systems. | Standards-based identity, short-lived scoped credentials, and session controls. |
| Excessive permissions | An identity, agent, or tool accesses more data or performs more actions than needed. | Least privilege, explicit per-tool permissions, and read-only boundaries. |
| Prompt and context injection | Untrusted content, metadata, or tool output influences unsafe behavior. | Treat external content as untrusted, validate outputs, restrict capabilities, and require approval for high-impact actions. |
| Malicious inputs and outputs | Malformed or unexpected data reaches tools or downstream services. | Schema validation, type checks, allowlists, sanitization, and payload limits. |
| SSRF, execution, and data leakage | A tool reaches internal services, executes an unsafe operation, or discloses sensitive context. | Restricted egress, isolation, minimal privileges, data-sharing boundaries, and monitoring. |
| Supply-chain and visibility gaps | A compromised component goes undetected, or teams cannot reconstruct activity. | Component review, scanning, centralized audit logs, and anomaly detection. |
Secure the HTTP transport and endpoint
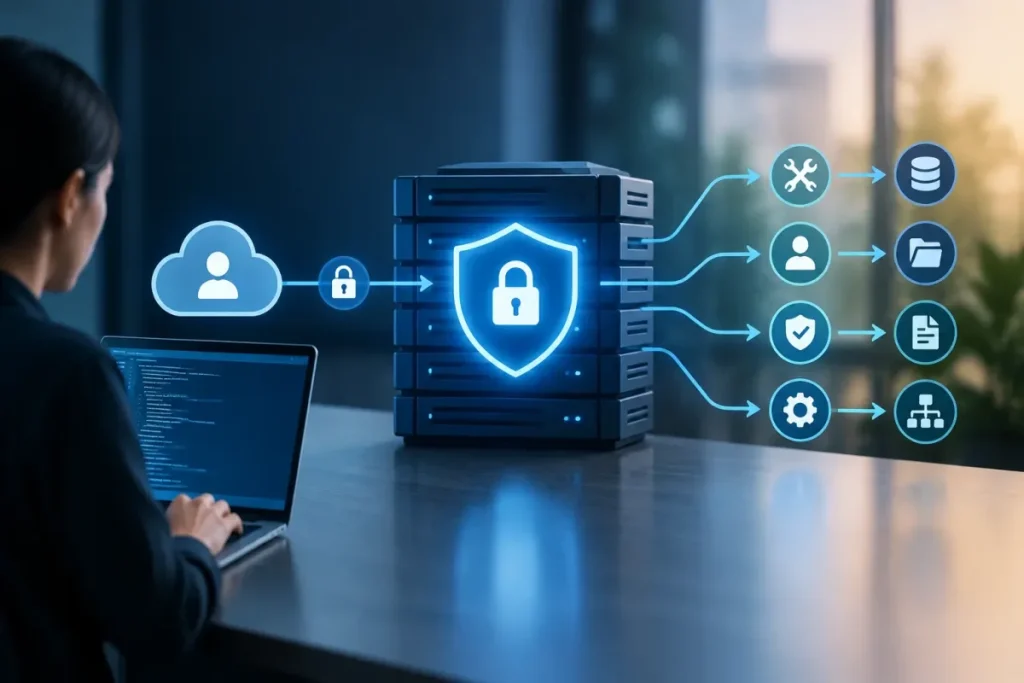
Enforce HTTPS/TLS for HTTP-facing MCP deployments. Where appropriate, place the endpoint behind an authenticated gateway, security proxy, or equivalent access-control layer. Private networking, firewalls, and segmentation can reduce unnecessary exposure to the public internet.
HTTPS alone does not solve MCP security. TLS protects data in transit, but it does not decide which client may invoke a tool, whether a token is valid, whether an agent is overprivileged, or whether a tool output contains malicious instructions.
Expose only the servers and capabilities the deployment requires. Review endpoint exposure, session expiration and invalidation, replay resistance, and the gateway’s policy configuration. Exact methods, headers, session lifecycles, and replay controls depend on the deployment architecture and require separate verification.
Use strong authentication and protect tokens
Authentication requirements depend on the MCP transport and deployment architecture. Use standards-based identity appropriate to the environment, such as OAuth or OIDC, cryptographic identity, or workload identity. A static, shared credential should not be treated as sufficient protection for a production MCP server.
Prefer short-lived, narrowly scoped credentials
Limit credentials to the required audience, scope, tool set, or operation. Where the architecture supports it, separate identities for users, hosts, clients, agents, and services. Avoid long-lived credentials and avoid silently inheriting a broad human identity when a narrower workload identity is appropriate. For credential design details, see Short-Lived Tokens for AI Agents.
Validate the full credential lifecycle
Validate token integrity, issuer and audience where relevant, scopes, session state, expiration, and redirect URIs supported by the selected identity flow. Review how credentials are issued, stored, rotated, revoked, and invalidated after suspected compromise.
Apply least-privilege authorization
Authentication establishes who is connecting; authorization determines what that identity, agent, client, or tool may do. Apply least privilege with RBAC or equivalent fine-grained controls, and make permissions explicit rather than broad by default.
- Define permissions for each user, agent, client, and tool.
- Separate read-only operations from write, administrative, and state-changing operations.
- Limit access to the data sources and external systems required for the task.
- Include tool discovery and tool chaining in authorization decisions.
- Do not automatically grant an agent every permission available to the person who started the task.
An agent authorized to use one tool should not automatically gain unrelated tools or broader privileges through a chain of calls. Sensitive operations need policy controls beyond the initial authenticated identity.
Validate requests, context, and tool outputs
Validate schemas and arguments
Validate JSON-RPC messages and tool arguments against tool-specific schemas. Use type checks, allowlists, sanitization, payload limits, and control-character filtering. Reject malformed or unexpected values before they reach a tool or downstream service.
Validate results as well as requests. Check that tool outputs match expected types and structures before an agent uses them in a later decision or tool call.
Treat external context as untrusted
Tool descriptions, metadata, retrieved content, external context, and tool outputs can contain instructions that influence agent behavior. Treat them as untrusted data, not authoritative policy.
Prompt or context injection is important, but it is not the only MCP security risk. Reduce its impact by separating instructions from untrusted content, limiting tool permissions, validating outputs, constraining data flows, and requiring approval before high-impact actions. No single filtering or validation control eliminates all injection risk.
Limit data exposure and unsafe actions
Set data-sharing boundaries
Decide which tools and external services may receive sensitive context. Prevent unnecessary sharing of confidential records, credentials, internal instructions, or user data with unapproved destinations. Review whether monitoring data and logs contain sensitive context as well.
Data leakage can occur through an inappropriate tool, external service, compromised component, or insecure log. Authorization, isolation, and monitoring should therefore work together.
Require approval for high-impact operations
Require human approval or step-up authorization before destructive, financial, credential-related, or otherwise high-impact actions. This includes changing important records, granting access, deleting data, or affecting production systems.
Approval gates reduce the chance that a mistaken, manipulated, or overconfident agent immediately performs a damaging action. They do not replace authorization, validation, logging, or monitoring.
Isolate servers and restrict network access
Run MCP servers and connected tools in controlled, minimally privileged environments. Depending on the architecture, this may involve private networking, containers, namespaces, firewalls, or other supported controls. Do not assume that a container or network boundary is correctly configured without verification.
Restrict unnecessary outbound access from MCP servers and tools. Review whether a component can reach internal metadata services, sensitive network locations, or unrelated enterprise systems. These controls help protect internal services against SSRF and limit unwanted tool calls.
Command and code-execution scenarios also belong in the threat model when connected tools can perform operations. Isolation, reduced privileges, network restrictions, and strict tool authorization help limit the blast radius, but their effectiveness must be tested for each implementation.
Govern third-party components and changes
Maintain an approved inventory of MCP servers, tools, identities, dependencies, and connected systems, including local, remote, and third-party components. Record ownership and intended use so unapproved deployments can be identified.
Review tool descriptors, dependencies, configurations, artifacts, and updates before they enter a production workflow. A compromised or misleading component can manipulate agent behavior, intercept requests, or expose data even when the HTTP endpoint is configured correctly.
Use trusted or verified components and include MCP-specific scanning in CI/CD where appropriate. Scan again after material changes to servers, tools, dependencies, permissions, or connected systems.
Centralize logging and detect anomalies
Record security-relevant MCP activity in centralized, protected logs. Capture, as appropriate to the deployment:
- the identity of the user, client, agent, or service;
- the MCP server and tool invoked;
- the requested data or operation;
- authorization and policy decisions;
- successes, failures, errors, and outcomes; and
- relevant authentication, configuration, and security events.
Protect logs against unauthorized access and alteration while minimizing unnecessary sensitive context. Use monitoring and anomaly detection to identify unusual tool combinations, unexpected data access, repeated authorization failures, sudden changes in call volume, or behavior that differs from an agent’s normal workflow.
Sequence-level monitoring matters because an individual call may appear legitimate while the chain of calls is not.
Pre-production checklist
- Transport: HTTPS/TLS is enforced, and unnecessary public exposure is reduced with suitable gateways, proxies, and network controls.
- Identity: The authentication model fits the transport and architecture; credentials are short-lived, narrowly scoped, and not unnecessarily shared.
- Sessions and tokens: Scope, redirect-URI, expiration, invalidation, session, and replay-related controls have been reviewed.
- Authorization: Per-user, per-agent, per-client, and per-tool permissions follow least privilege, with clear read-only and administrative boundaries.
- Validation: Messages, schemas, types, arguments, payload sizes, context, and tool outputs are handled as untrusted input.
- Data protection: Sensitive context is limited to approved tools and services, and logs do not expose unnecessary confidential data.
- Isolation: Servers and tools run in controlled environments with restricted outbound access and no unnecessary internal connectivity.
- Approvals: Destructive, financial, credential-related, and other high-impact operations require human approval or step-up authorization.
- Governance: Servers, tools, identities, dependencies, descriptors, and connected systems are inventoried and reviewed.
- Monitoring: Tool calls, identities, requested data, decisions, outcomes, errors, and security events are centrally logged and monitored for anomalies.
- Scanning and testing: Servers, dependencies, configurations, and changes are scanned and tested before deployment and after material changes.
- Response readiness: The team has verified how it will respond to credential compromise, context leakage, rogue servers, tool poisoning, and destructive actions.
Before implementation, separately verify the HTTP configuration, session lifecycle, replay resistance, SSRF controls, internal-network restrictions, command or code-execution boundaries, rate thresholds, log retention, privacy handling, testing approach, and MCP-specific incident-response procedures. These details vary by architecture and are not solved by a generic checklist. For a broader implementation checklist, see MCP Security Checklist for Clients and Servers.
Final takeaway
MCP HTTP exposure is not safe by default. Effective MCP security requires layered protection: HTTPS and network controls, strong identity, short-lived credentials, least-privilege authorization, strict validation, controlled data flows, isolated deployments, human oversight, supply-chain governance, and centralized monitoring.
Use the checklist as a starting point, then verify implementation-specific controls in an isolated environment. The goal is to limit what an exposed MCP workflow can reach, do, disclose, and conceal.