
Short-lived token checklist
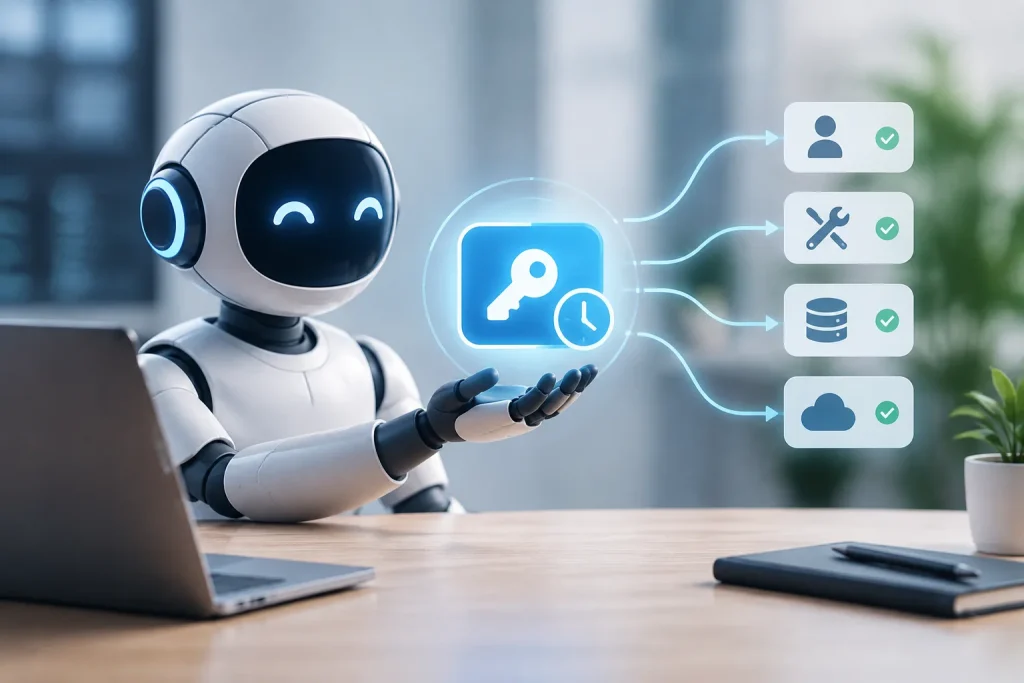
- Short-lived tokens for AI agents are temporary, task- or session-scoped access credentials that expire automatically—typically after minutes or hours—and are used to reduce the exposure and blast radius of compromised agent access. They should be narrowly scoped, issued just in time to a dedicated agent identity, and revoked when practical; they are a risk-reduction control rather than a complete security solution.
- Use an identity provider or credential broker to issue tokens just in time.
- Apply least-privilege scopes for the exact tools, APIs, or operations required.
- Use dedicated, auditable agent identities instead of human credentials or shared static keys.
- Set the shortest practical TTL based on task duration and privilege, and revoke tokens after completion when supported.
Short-lived tokens for AI agents are temporary, task- or session-scoped access credentials that expire automatically—typically after minutes or hours—to reduce the exposure and blast radius of compromised agent access.
They should use narrow permissions, belong to a dedicated agent identity, be issued just in time, and be revoked when practical. They are a risk-reduction control, not a complete security solution.
What are short-lived tokens for AI agents?
A short-lived token is an authentication or authorization credential with a limited lifetime. It gives an AI agent access to a specific tool, API, resource, or operation for a defined task or session, then stops working automatically when it expires. For a deeper explanation of how scoped credentials are issued and delegated, see OAuth for autonomous AI agents.
The appropriate lifetime depends on the task duration, privilege, and system risk. A token may remain valid for minutes or hours, but no single expiration period fits every agent or workflow.
Two controls work together:
- Expiration limits how long the credential can be used.
- Scope limits what the credential can access or do.
The goal is to give an agent only the access it needs, for only as long as it needs it.
Access credentials versus LLM text tokens
For AI-agent authentication, “token” means an access credential for an AI agent—not the LLM text tokens counted as model input and output or used in model pricing.
LLM text tokens describe how a model processes inputs and responses. Security tokens support authentication and authorization: they help a tool, API, or service determine whether an agent may perform an operation.
The two concepts can exist in the same workflow, but they solve different problems. Reducing LLM token usage does not replace temporary credentials, and expiring an access token does not reduce the number of text tokens a model processes.
Why use short-lived tokens?
Reduced exposure window
If an agent or its credential is compromised, automatic expiration limits how long the access can remain useful. A credential that expires during or shortly after a task creates a smaller exposure window than one that remains valid indefinitely.
Smaller potential blast radius
A short lifetime can reduce the potential damage window after a compromise. It does not make compromise impossible; it limits the period in which the compromised credential can be used.
Narrower permissions
Short-lived tokens should be limited to the specific tools, APIs, resources, or operations required for the task. Narrow permissions reduce the access available to an agent compared with broad, all-access credentials. For a broader guide to assigning permissions and guardrails, see autonomous AI agent authorization.
Lifetime and authorization scope should be considered together. Higher-privilege access generally calls for the shortest practical lifetime that still allows the task to finish.
Clearer agent identity separation
Issuing a token to a dedicated AI-agent identity separates agent activity from a person’s credentials. It also makes that activity easier to attribute and review than access performed through a shared key or a human user’s primary credentials. For guidance on authenticating an agent as a distinct workload identity, see autonomous AI agent authentication.
How should short-lived tokens be implemented?
Issue credentials just in time
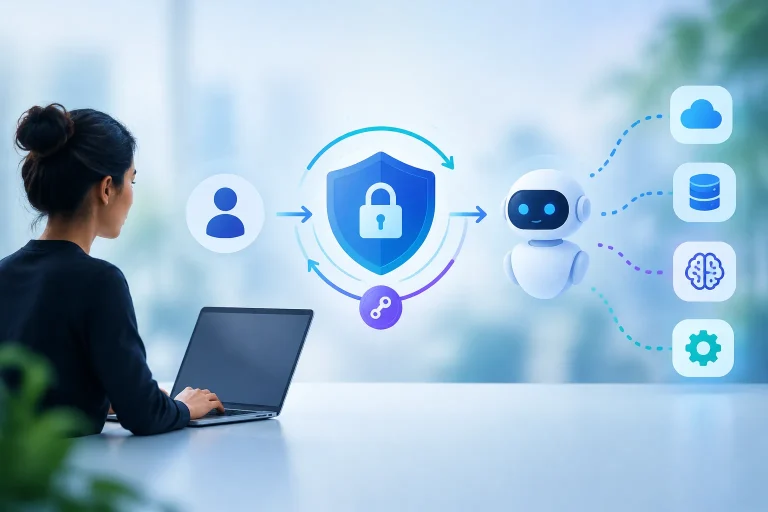
Use an identity provider or credential broker to issue an agent credential when it is needed for a task, rather than supplying a persistent credential in advance. Just-in-time issuance ties the credential lifecycle to the work being performed.
Apply least-privilege scopes
Limit each token to the exact tools, APIs, resources, or operations required. Avoid broad permissions when a narrower scope can support the task. An agent should not receive access simply because it might need it later.
Use dedicated, auditable agent identities
Issue credentials to a dedicated agent identity instead of allowing an agent to use a person’s credentials. Do not rely on shared static keys or a human user’s primary credentials for routine agent access. For help choosing between temporary delegated access and static credentials, see OAuth versus API keys for AI agents.
A distinct identity makes it clearer which activity belongs to the agent and supports audit records for issuance, use, expiration, and revocation.
Set the shortest practical lifetime
Configure automatic expiration for every short-lived credential. Choose the shortest practical duration based on task length, privilege, and system risk; do not apply one universal expiration period to every agent or operation.
If a task needs more time, handle renewal deliberately rather than relying on a broad, persistent key. When supported, issue a replacement credential through the same controlled process.
Revoke credentials after completion
When supported, revoke the token after the task is complete instead of waiting for normal expiration. Revocation adds a lifecycle control, while automatic expiration remains the backstop.
Maintain auditability and approval
Record token issuance, use, expiration, and revocation so agent activity can be reviewed. For high-impact or high-privilege actions, require human approval before the action or credential release when appropriate to the system’s risk.
Short-lived tokens in multi-agent workflows
When multiple agents or subagents access tools, each should receive access appropriate to its own task rather than relying on one broad credential shared across the workflow.
Separate agent identities and narrow scopes keep delegated work attributable and limit each credential to the operations it requires. The lifetime should also match the individual task: a short subtask does not need the same access duration as a longer-running operation.
What short-lived tokens do not solve
A short-lived token is not automatically safe. While it is valid, an agent may still have excessive permissions, use an inappropriate tool, or perform an unintended action.
Expiration does not eliminate every agent-security risk. Use temporary credentials alongside least-privilege authorization, dedicated identities, auditability, revocation, and approval controls.
The specific role of a short-lived token is to limit the duration and scope of access—not to provide complete protection.
Short-lived token implementation checklist
- Automatic expiration: Each token stops working after a defined, limited lifetime.
- Appropriate lifetime: The TTL matches task duration, privilege, and system risk rather than a universal default.
- Least privilege: Scopes cover only the required tools, APIs, resources, or operations.
- Dedicated identity: The credential belongs to an auditable agent identity, not a human user or shared static key.
- Controlled lifecycle: Issuance is just in time where supported, and revocation follows completion when available.
For high-impact or high-privilege actions, add human approval and maintain records of credential activity. The central principle is simple: give the agent only the access it needs, for only as long as it needs it, and treat short-lived access as risk reduction rather than complete protection.