
Assessment, penetration test, or both?
- Use an AI security assessment for pre-launch reviews, governance or compliance needs, architecture and control evaluation, lifecycle risk, privacy, and vendor or deployment-risk analysis.
- Use an AI penetration test when the goal is to simulate attacks and validate whether AI-specific weaknesses can be exploited.
- Combine both when an organization needs holistic assurance plus evidence of real-world exploitability.
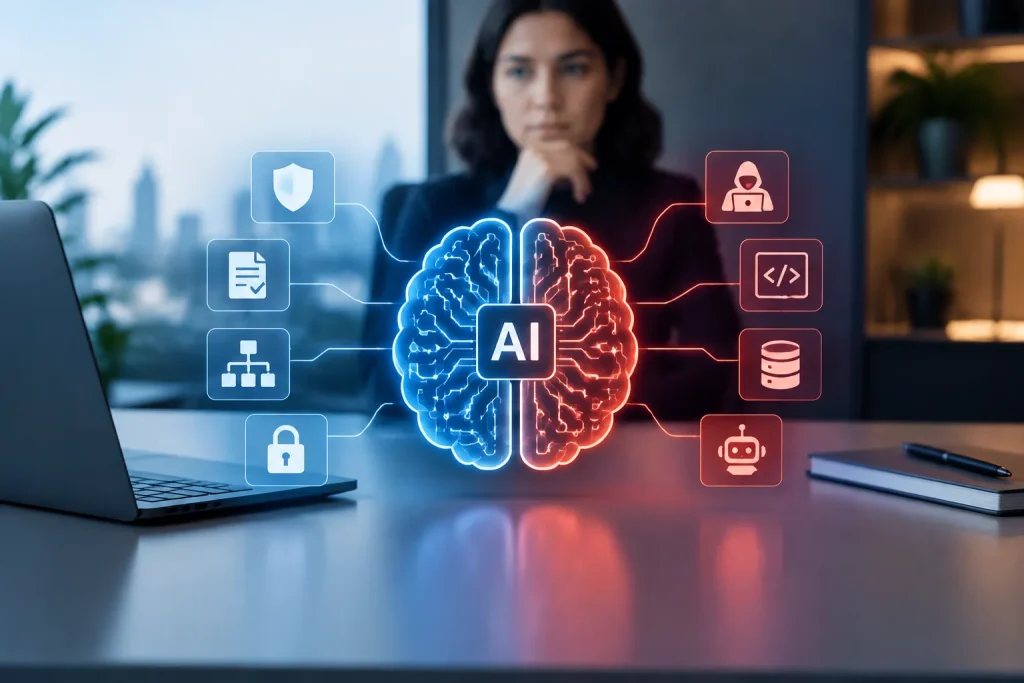
An AI security assessment is a broad evaluation of an AI system’s security, governance, architecture, privacy, compliance, and controls. An AI penetration test is a hands-on offensive test that probes and attempts to exploit weaknesses in models, prompts, RAG pipelines, APIs, tools, and agent behavior. They are complementary: choose an assessment, a penetration test, or both.
AI Security Assessment vs AI Penetration Test: The Short Answer
The core distinction is broad posture evaluation versus active exploit validation:
- An AI security assessment reviews the system’s architecture, governance, privacy, compliance, lifecycle processes, risks, and security controls.
- An AI penetration test simulates authorized attacks to determine whether technical weaknesses in AI components and connected systems can actually be exploited.
- The approaches are complementary, not interchangeable. Organizations seeking comprehensive assurance may need both.
Choose an assessment for pre-launch readiness, governance, privacy, compliance, architecture, lifecycle, vendor, or deployment-risk questions. Choose a penetration test when the priority is attack simulation and evidence of exploitability. Use both when you need broad control evaluation and deep technical validation.
What Is an AI Security Assessment?
An AI security assessment is a systematic review of an AI system’s security posture and the controls intended to manage its risks. It considers how the system is designed, operated, governed, integrated, monitored, and changed over time.
Typical assessment scope
Depending on the architecture and engagement objectives, an assessment may examine:
- Models and model-related services
- Prompts, instructions, application logic, and trust boundaries
- Data sources, retrieval components, vector stores, and RAG pipelines
- APIs, tools, agents, and external integrations
- Training, processing, deployment, and data pipelines
- Access controls, security architecture, and supporting infrastructure
- Governance, privacy, compliance, monitoring, and lifecycle processes
- Vendor, deployment, and operating-environment risks
The work may include documentation and control reviews, interviews, architecture and data-flow analysis, risk analysis, and targeted validation. Its emphasis is understanding whether the system’s controls and operating model support its security objectives—not only finding a path to compromise.
What an assessment does not prove
An assessment does not necessarily prove that a reported weakness is exploitable. It may identify a risky design, missing control, privacy concern, governance gap, or architectural weakness without reproducing an attack against the live system.
That does not make an assessment a checklist exercise. Its broader perspective can identify risks that a focused attack exercise may not cover. However, compliance alignment or documented controls should not be treated as proof that the system is secure or that every vulnerability is exploitable.
What Is an AI Penetration Test?
An AI penetration test is an authorized, hands-on offensive exercise that simulates attacks against an AI or machine-learning system. Active probing and exploitation are its defining characteristics. The goal is to determine whether technical weaknesses are exploitable and what impact they could have.
Depending on scope, testing may target models, prompts, retrieval or RAG components, APIs, tools, agents, data flows, pipelines, integrations, deployment architecture, and supporting infrastructure. Coverage depends on the system, access provided to testers, business objectives, and rules of engagement.
Potential AI attack surface
High-level areas of authorized testing can include:
- Model behavior and adversarial inputs
- Direct and indirect prompt injection
- Jailbreaks and policy-boundary weaknesses
- Data exposure through responses, retrieval, or integrations
- Data poisoning and weaknesses in data or processing pipelines
- Model inversion or model extraction risks
- API authentication, authorization, sessions, and endpoint relationships
- Agent manipulation and excessive agency
- Tool misuse, unsafe permissions, and backend integration flaws
- Multi-step workflows in which individually permitted actions create a harmful chain
AI penetration testing is not limited to isolated prompt testing. A properly scoped engagement can examine how the model interacts with application logic, retrieval sources, APIs, tools, users, and other systems.
Exploit validation
Penetration testers investigate whether a suspected weakness is realistic and impactful under the agreed authorization. High-level techniques may include attack-surface mapping, adversarial inputs, fuzzing, attack simulation, state-aware workflow testing, and controlled exploit validation.
The result is evidence about exploitability, not merely the existence of a theoretical issue. This helps security teams prioritize remediation and distinguish practical attack paths from findings without meaningful impact. Testing should remain bounded by the rules of engagement and avoid unnecessary impact on production systems.
AI Security Assessment vs AI Penetration Test: Side-by-Side Comparison
| Area | AI security assessment | AI penetration test |
|---|---|---|
| Primary objective | Evaluate overall security posture, risk, governance, architecture, privacy, compliance, and controls. | Determine whether technical weaknesses can be actively exploited. |
| Scope | Broad review of the AI system and its lifecycle, including models, data, integrations, processes, and supporting controls. | Focused offensive testing of selected models, prompts, retrieval, APIs, tools, agents, workflows, and infrastructure. |
| Approach | Documentation and control review, architecture analysis, lifecycle review, risk analysis, and targeted validation. | Attack-surface mapping, adversarial testing, attack simulation, fuzzing, workflow testing, and exploit validation. |
| Active exploitation | May include limited validation but is not defined by exploitation. | Active probing and exploitation are defining activities. |
| Evidence | Risk, control, posture, architecture, governance, privacy, and compliance-related findings. | Validated weaknesses, attack evidence or narratives, impact analysis, and applicable retesting results. |
| Typical outputs | Prioritized posture findings, control observations, risk conclusions, and improvement recommendations. | Technical findings tied to exploitability, impact, remediation guidance, and retesting where included. |
| Governance and compliance usefulness | Useful for reviewing obligations, processes, and related controls, without treating alignment as proof of security. | Useful as technical evidence of selected weaknesses, but not a complete governance, privacy, or compliance review. |
| Best fit | Organizations seeking holistic assurance and a broad view of security readiness. | Organizations seeking evidence of what an attacker may be able to exploit. |
The same component may appear in both engagements but be examined differently. An assessment may review whether an agent has appropriate permissions and oversight. A penetration test may attempt to manipulate that agent into misusing an authorized tool.
Assessment Methods vs Penetration-Test Methods
Assessment methods
- Reviewing system documentation, policies, and security controls
- Analyzing architecture, data flows, integrations, and trust boundaries
- Reviewing governance and lifecycle processes
- Evaluating privacy, compliance, access, monitoring, and risk-management practices
- Identifying control gaps, design risks, and remediation priorities
- Using limited validation to confirm a control or architectural conclusion
This approach evaluates the wider environment and its risk-management capability. It can uncover problems that do not require an attacker to demonstrate a working exploit, such as weak oversight, unclear ownership, inappropriate permissions, or missing lifecycle controls.
Penetration-test methods
- Mapping the authorized attack surface
- Reviewing exposed models, prompts, APIs, retrieval sources, tools, and workflows
- Applying adversarial inputs and controlled attack simulations
- Testing state-aware, multi-step behavior across related endpoints or actions
- Using fuzzing or structured input variation
- Testing authorization boundaries and tool permissions
- Validating whether suspected weaknesses are exploitable and meaningful
The exact method depends on access, environment, objectives, and safety requirements. Black-box, white-box, or hybrid access can change what testers evaluate, but the central goal remains technical exploit validation.
Vulnerability Scanning Is Not Penetration Testing
Vulnerability scanning generally compares systems with known issues, signatures, rules, or defined input patterns. It can identify potential weaknesses efficiently, but a scanner does not necessarily understand application logic, state, permissions, or chained behavior.
An AI penetration test goes further by simulating attacks, exploring system behavior, and validating whether a weakness can produce a realistic impact. Scanning is identification-oriented, penetration testing is exploitation-oriented, and an assessment evaluates the wider posture and control environment.
AI-Specific Testing and Conventional Security Testing
Traditional application, API, cloud, and infrastructure testing remains relevant. Conventional testing can examine networks, servers, applications, authentication, authorization, and exposed interfaces. AI penetration testing adds examination of model behavior, prompts, data, retrieval, agents, algorithms, and AI-specific attack paths.
An AI-specific engagement should not be treated as an automatic substitute for testing the application, API, cloud, or infrastructure components on which the AI system depends.
Deliverables, Evidence, and Remediation
An assessment generally produces findings about risk, controls, posture, architecture, governance, privacy, compliance, and priorities. Its conclusions help decision-makers understand what should be improved and which risks require treatment.
A penetration test generally produces findings tied to validated technical weaknesses. Depending on the engagement, findings may include:
- A description of the weakness and affected component
- An attack narrative or other evidence of exploitability
- Impact and severity treatment
- Remediation guidance
- Retesting results after fixes are implemented, where retesting is included
Report structures, scoring methods, formal mappings, and deliverable formats vary by provider and engagement. They should be agreed before work begins rather than assumed from the service name.
Remediation should match the finding. A governance gap may require a policy, ownership, or process change. An exploitable API or agent weakness may require code, permission, architecture, or configuration changes. In both cases, teams should define owners and priorities clearly.
When to Choose an Assessment, a Penetration Test, or Both
Choose an AI security assessment when:
- The AI system is approaching launch and its broad readiness needs review.
- Leadership needs a view of governance, architecture, privacy, compliance, or lifecycle risk.
- The organization is evaluating a vendor, deployment model, or major integration.
- Security teams need to understand controls and priorities before deeper technical testing.
- The main question is whether the overall security posture is appropriate for the system’s use.
Choose an AI penetration test when:
- The priority is hands-on attack simulation.
- The organization needs to validate whether AI-specific weaknesses are exploitable.
- A model, RAG pipeline, API, agent, tool, or integration has changed significantly.
- Security teams need technical evidence to prioritize or verify remediation.
Use both when:
The organization needs broad control and lifecycle assurance together with evidence of real-world exploitability. The assessment can identify risks outside the scope of an attack exercise, while the penetration test can validate whether selected technical weaknesses can be used in practice.
Neither approach universally replaces the other. Comprehensive coverage may also require conventional application, API, cloud, and infrastructure testing alongside AI-specific work.
Reassessment, Automation, and Human Expertise
Reassess after meaningful changes
AI systems should be reassessed after significant changes to the model, data, integrations, deployment architecture, or operating environment. A product change can alter permissions, data exposure, model behavior, or the available attack surface.
Recurring assessment activities and suitable penetration-testing or regression checks may be integrated into CI/CD or MLOps workflows. The appropriate schedule depends on risk, change velocity, architecture, and available safeguards rather than a universal calendar.
Automation supports—but does not replace—human expertise
AI-assisted testing can improve speed, scale, consistency, and continuity. Automated processes can repeat checks, explore large numbers of inputs, and support regression testing as systems change.
Human security professionals remain important for:
- Understanding business context and acceptable impact
- Reviewing architecture and trust boundaries
- Recognizing novel or unusual threats
- Connecting separate weaknesses into a complex attack chain
- Assessing business logic and authorization decisions
- Interpreting evidence and validating remediation
A hybrid model combines automated breadth with human judgment. It should be selected according to the system’s complexity, risk, rate of change, and engagement objectives.
Practical Engagement Checklist
Before commissioning either service, define the engagement in writing. Clarify:
- Objectives: Are you evaluating broad posture and controls, exploitability, or both?
- Assets: Which models, prompts, applications, APIs, data stores, retrieval sources, agents, tools, pipelines, and environments are included?
- Access: Which accounts, roles, credentials, documentation, source code, or architecture details will testers receive?
- Environment: Will testing occur in development, staging, production, or more than one environment?
- Integrations: Which vendors, external services, APIs, cloud resources, and downstream systems are in scope?
- Success criteria: What questions must the engagement answer, and what evidence is required?
- Rules of engagement: Which activities are authorized, prohibited, rate-limited, or subject to approval?
- Production safeguards: How will sensitive data, availability, transactions, and external side effects be protected?
- Severity handling: How will findings be prioritized and escalated?
- Remediation: Who owns fixes, what timelines apply, and how will closure be determined?
- Retesting: Is validation after remediation included, and which findings will be retested?
Ask providers to state clearly whether the engagement is primarily review-oriented or exploit-oriented. Require them to identify out-of-scope components so that a limited test is not mistaken for comprehensive assurance.
Frequently Asked Questions
What is the difference between a penetration test and a security assessment?
A security assessment evaluates broader risk, controls, architecture, governance, privacy, compliance, and lifecycle posture. A penetration test actively simulates attacks and attempts to exploit technical weaknesses. An assessment may include limited validation, but active exploitation defines the penetration test.
What does AI penetration testing examine?
Depending on scope, it can examine models, prompts, RAG or retrieval components, APIs, data flows, tools, agents, integrations, pipelines, and deployment architecture. Potential attack categories include prompt injection, jailbreaks, data exposure, model extraction or inversion, API abuse, agent manipulation, excessive agency, and tool misuse.
Can AI-powered testing replace human security professionals?
No. Automation can improve speed, scale, consistency, and continuity, while human expertise remains necessary for business context, architecture, novel threats, complex attack chains, judgment, and validation.
What are the three main types of security assessments?
There is no single three-part classification established for every organization or engagement. Assessment categories vary by objective, such as evaluating broad posture and controls or validating technical exploitability. Define the assurance question first rather than forcing an engagement into an unsupported fixed taxonomy.
Conclusion
An AI security assessment evaluates broad security posture, architecture, governance, privacy, compliance, controls, and lifecycle risk. An AI penetration test actively probes and attempts to exploit technical weaknesses in AI systems and their surrounding workflows.
Use an assessment for holistic assurance, a penetration test for exploitability evidence, and both when you need broad control evaluation plus hands-on technical validation. Supplement AI-specific work with conventional application, API, cloud, or infrastructure testing wherever those parts of the environment are relevant.