
Secure default for authenticating an autonomous AI agent
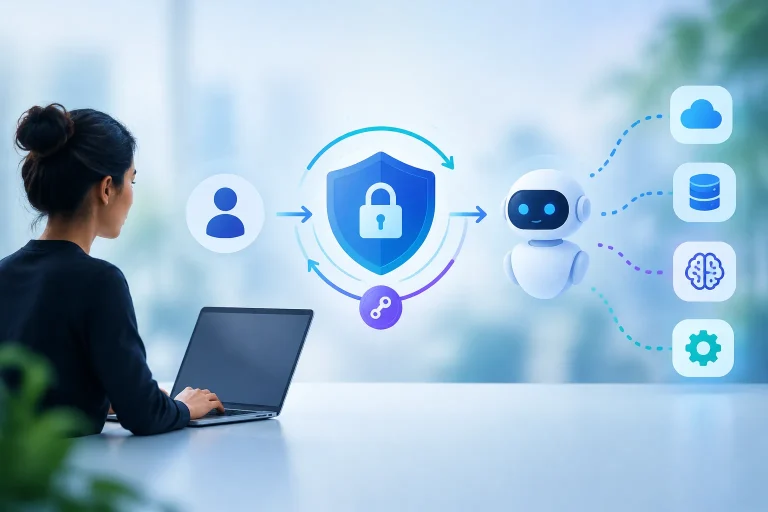
- Authenticate the agent as a distinct non-human workload identity using standard machine-authentication mechanisms—prefer short-lived, narrowly scoped OAuth/M2M tokens, workload identity, or certificates where supported—and then enforce least-privilege authorization, rotation, audit logging, and rapid revocation. Use delegated or on-behalf-of tokens when the agent acts for a user, and require human approval for high-risk actions.
- OAuth 2.1 or machine-to-machine client credentials with short-lived, scoped tokens.
- Workload identity or attestation-backed ephemeral credentials, including SPIFFE/SPIRE-style approaches where applicable.
- mTLS or X.509 certificates for service-to-service agent authentication.
- Service accounts with tightly scoped, rotatable credentials when workload identity is unavailable.
Authenticate an autonomous AI agent as a distinct non-human workload identity using short-lived, narrowly scoped OAuth/M2M tokens, workload identity, or certificates where supported. Then enforce least-privilege authorization, rotation, audit logging, rapid revocation, delegated access when needed, and human approval for high-risk actions.
Direct answer: use this security sequence
- Create and register a distinct agent identity for each deployed agent or workload.
- Issue a cryptographically verifiable credential that fits its runtime and integrations.
- Prefer short-lived, narrowly scoped credentials over static or long-lived secrets.
- Enforce authorization separately from authentication, limiting tools, APIs, data, workflows, actions, and spending.
- Monitor activity, rotate or expire credentials, and maintain rapid revocation and emergency shutdown controls.
Use machine-to-machine client credentials when the agent acts as itself. Use OAuth authorization code with PKCE or a narrowly scoped on-behalf-of exchange when it acts for a user. Authentication proves which software entity is making a request; it does not authorize every action that entity requests.
What authentication means for an autonomous AI agent
Authentication verifies a non-human software entity before it accesses an API, tool, service, dataset, workflow, or infrastructure resource. The identity should belong to the deployed agent or workload—not to the language model in isolation and not to an employee whose credentials were shared with it.
Authentication versus authorization
Authorization is the separate decision about what an authenticated agent may do. Server-side policy should determine which tools, APIs, records, workflows, actions, and spending limits are available. A valid token must never be treated as permission for unrestricted operations.
Delegation versus impersonation
Delegation gives an agent limited authority to act for a user within an approved scope. Impersonation gives it the user’s identity and potentially broader authority. Prefer down-scoped delegated tokens and task-specific permissions instead of copying or sharing a user’s credentials.
Why the LLM is not the identity
The model generates or helps select actions, but it is not a durable, accountable security principal. The deployable agent, service, or workload that executes requests needs its own registered identity, owner, permissions, lifecycle, and audit trail.
Step 1: Create and govern the agent identity
Register one identity per deployed agent
Create a distinct identity for each deployed AI agent or meaningfully separate workload. Avoid shared credentials across agents. Per-agent identities improve attribution, permission management, revocation, and investigation when access or behavior is questioned.
Assign ownership and intended scope
Record the accountable owner, purpose, expected tools and resources, delegation model, credential requirements, and operating environment. The identity should have a defined lifecycle covering:
- Provisioning and approval
- Credential issuance and permission changes
- Monitoring and review
- Rotation, revocation, and decommissioning
An autonomous agent should not use a human password, personal access token, or general-purpose session. When a user initiates work, represent that relationship through an explicit delegated flow with limited permissions and an appropriate expiration.
Step 2: Choose the authentication method
No single protocol fits every autonomous agent. Choose according to whether it acts as itself or for a user, where it runs, which trust boundary it crosses, how finely permissions must be scoped, and how quickly access must be revoked.
OAuth 2.1 and machine-to-machine client credentials
Use the client-credentials flow when the agent acts as itself in machine-to-machine access. It presents its client identity to obtain a token for a specific resource, then calls the API with that token.
Prefer short-lived tokens with narrow scopes and an intended audience or resource. This is generally more suitable than a reusable static secret when the authorization server and target API support it. For more on reducing exposure with temporary credentials, see short-lived tokens for AI agents.
OAuth authorization code with PKCE
Use authorization code with PKCE when a user must authorize delegated access. Keep the resulting access limited to the user’s approved scope and the agent’s task. This is a delegated-user flow, not the default method for an agent accessing an internal service as itself. For MCP-specific handling of this delegated flow, see MCP OAuth security guidance.
Workload identity
Use workload identity when the runtime can obtain credentials based on where and how the workload is running, rather than depending on a long-lived secret in configuration. It is a strong fit for managed or orchestrated workloads when the platform can establish the workload’s identity and support its lifecycle.
mTLS and X.509 certificates
Mutual TLS (mTLS) authenticates both sides of a service-to-service connection with digital certificates. It suits supported internal environments where certificate issuance, deployment, renewal, validation, and revocation can be operated reliably.
Service accounts
Use a service account when workload identity is unavailable or an integration requires one. Give it only the permissions required by the agent, use separate accounts where attribution matters, and rotate or expire its credentials. A service account is an identity model, not a reason to grant permanent or unrestricted access.
API keys
API keys remain common for third-party APIs, but static or reusable keys are generally weaker than short-lived, scoped credentials. They can be difficult to scope precisely, vulnerable to leakage, and harder to revoke safely. For a fuller comparison of these credential choices, see OAuth vs API keys for AI agents.
If an API key is necessary:
- Use a separate key for each agent or integration.
- Restrict permissions and resources as narrowly as the provider allows.
- Store it in protected application configuration, never in prompts or agent instructions.
- Limit its lifetime where supported.
- Monitor for exposure and unusual use.
- Rotate it and maintain a rapid revocation procedure.
Method-selection guide
| Agent situation | Preferred method | Key controls |
|---|---|---|
| Agent acts as itself against an API or internal service | OAuth client credentials or another M2M token | Short lifetime, narrow scope, intended audience, server-side authorization, logging, and revocation |
| Agent accesses resources for a user | OAuth authorization code with PKCE | Explicit user authorization and limits matching the approved task |
| Agent passes a user’s authority through a service chain | On-Behalf-Of token exchange | Narrow delegation rather than unrestricted user impersonation |
| Managed or orchestrated workload | Workload identity | Runtime binding and reduced dependence on static secrets |
| Internal service-to-service environment | mTLS or X.509 certificates | Reliable certificate issuance, renewal, validation, and revocation |
| API supports only shared secrets | Scoped API key or service-account credential | Smallest permission set, protected storage, monitoring, rotation, and rapid revocation |
Evaluate each option against the deployment environment, trust boundary, delegation model, interoperability requirements, scope granularity, credential lifetime, revocation needs, and operational burden. A method that is strong in theory can still be unsafe if the team cannot monitor, rotate, or revoke it reliably.
Step 3: Separate authentication from authorization
Use least-privilege scopes
Grant the minimum access required for the agent’s actual work. Restrict not only which API it can call, but also which records it can read, tools it can invoke, actions it can perform, and workflows it can start.
Add task, audience, and spending limits
Where applicable, define limits for a particular task, transaction type, destination, time window, or amount. Bind tokens to the intended audience or resource. These limits must be enforced by the resource server or policy engine; a prompt is not a security boundary.
Control cumulative effects
Validate authorization at the resource server and at meaningful points in a tool chain. A sequence of individually permitted calls can still produce an unintended result, so controls should account for the task, accumulated effects, and resulting blast radius where practical.
Step 4: Handle delegated and agent-to-agent access
When the agent acts as itself
Use a workload identity, service account, certificate, or client-credentials token tied to the agent. Its own permissions determine what it can access. This is the normal model for scheduled jobs, internal automation, and service-to-service operations.
When the agent acts on behalf of a user
Use OAuth authorization code with PKCE when a user must authorize access. For a service chain in which one component passes the user’s authority to another, use an On-Behalf-Of exchange with a narrow, task-specific scope where supported. Keep both the agent identity and delegated user context visible for attribution.
When agents call other agents
Treat every agent in a multi-agent system as a separate security principal. Each agent should authenticate with its own credential, and the receiving agent should verify the caller, intended audience, requested capability, and delegation chain.
- Use signed requests or another cryptographically verifiable credential where supported.
- Pass only the authority required for the next task; do not forward a broad parent token by default.
- Attenuate scope at each handoff so a downstream agent cannot gain more permission than its caller.
- Record the originating user, each agent in the chain, the requested action, and the final result.
- Reject expired, replayed, cross-audience, or unapproved delegation attempts.
Agent-to-agent authentication does not replace authorization. The receiving agent must still apply its own policy before executing a request.
Step 5: Secure credentials and tokens
Prefer credentials that expire quickly enough to limit exposure. Rotate renewable credentials on a defined schedule and after suspected exposure. Keep secrets outside model instructions, prompts, conversation history, and ordinary application logs; provide only the minimum credential material needed for the authenticated operation.
- Use short lifetimes and narrow scopes.
- Store secrets in protected application configuration or an approved credential-management system.
- Use separate credentials per agent or integration.
- Support rotation without unnecessary service interruption.
- Maintain centralized revocation.
- Remove active access during decommissioning.
Assume a credential may eventually be exposed. Document who can revoke it, how replacement credentials are issued, how dependent services fail, and how affected activity is investigated. Test rapid revocation before an incident.
Step 6: Validate every meaningful request
Successful credential presentation is only the first check. Before allowing a tool call or sensitive operation, validate the identity, credential, requested resource, and context in which the agent is operating.
| Validation check | Question | Failure response |
|---|---|---|
| Registered identity | Is this agent known, active, and assigned to an accountable owner? | Deny the request and alert the owner or operator. |
| Credential or token | Is it valid, unexpired, issued for this use, and cryptographically verifiable where applicable? | Reject it; do not silently use a broader credential. |
| Audience and resource | Is the request intended for this API, tool, or service? | Deny cross-resource use and record the event. |
| Permissions | Does the scope permit this exact operation, resource, and task? | Block the action or require narrower authorization. |
| Ownership and delegation | If acting for a user, is the delegation valid and within that user’s boundary? | Stop the request rather than treating the agent as the user. |
| Runtime behavior | Does the request fit the agent’s expected tools, intent, and activity pattern? | Reduce privileges, pause the session, investigate, or revoke access. |
| Audit record | Can operators reconstruct the agent, user context, tool, action, resource, time, and result? | Do not permit sensitive automation without sufficient traceability. |
Step 7: Monitor activity and maintain emergency controls
Monitor more than login success. Useful signals include identity use, permission changes, prompts, tool calls, requested intent, access patterns, and behavioral anomalies. Maintain an audit trail linking each action to the agent identity and, where applicable, the delegated user.
Define responses for unusual or dangerous behavior:
- Temporarily reduce the agent’s permissions.
- Block a tool or resource.
- Require human review.
- Revoke the current credential or token.
- Terminate the session or activate an emergency shutdown control.
Test these controls. An emergency procedure that has never been exercised may fail when an autonomous process is making requests at speed.
Step 8: Add human approval for sensitive actions
Human approval is an additional control, not an authentication method. Require it for high-risk operations such as irreversible changes, sensitive data access, consequential transactions, or actions with material financial or operational impact.
Lower-risk work can remain autonomous when the agent’s identity, permissions, limits, monitoring, and revocation controls are working as intended. Place the approval gate before the sensitive action, show the relevant context, and prevent the agent from bypassing the decision through another tool or service.
Authenticated agent-to-tool access with MCP
MCP can support authenticated agent-to-tool integration, capability discovery, and scoped tool invocation. Use this sequence:
- Establish the agent’s identity with an appropriate credential.
- Authenticate the connection to the tool service.
- Discover available capabilities without treating discovery as permission.
- Apply server-side authorization to the specific tool, parameters, resource, and task.
- Invoke only the approved capability and record the request and result.
- Retain monitoring, revocation, and human approval for sensitive operations.
Tool descriptions and other external content can create prompt-injection risk. Instructions supplied by a tool must not override identity, authorization, or safety policy. A discovered capability is not automatically an approved capability.
How to select an implementation or provider
There is no universally best provider for every autonomous agent. Select an implementation that supports the required protocols and operational controls rather than choosing by product name alone.
- Support for short-lived, scoped machine credentials and delegated access
- Workload identity, certificates, or other cryptographically verifiable identities where needed
- Server-side policy enforcement and scope attenuation across agent chains
- Centralized logging, monitoring, rotation, and rapid revocation
- Integration with the agent’s runtime, APIs, tools, and infrastructure
- Manageable operational burden and tested emergency procedures
Implementation checklist
- Create the identity: register one accountable, non-human identity for each deployed agent.
- Choose the method: use client credentials for agent-as-itself access; PKCE for delegated user access; on-behalf-of exchange for narrow service-chain delegation; workload identity or certificates where supported.
- Issue narrow credentials: prefer short-lived, cryptographically verifiable credentials and use API keys only when necessary.
- Enforce authorization: limit tools, APIs, data, actions, spending, workflows, and chained effects server-side.
- Validate requests: check identity, credential validity, audience, permissions, ownership, delegation, and runtime behavior.
- Protect the lifecycle: store credentials securely, rotate or expire them, monitor exposure, revoke centrally, and decommission them cleanly.
- Monitor and respond: log agent and tool activity, detect anomalies, test emergency controls, and support rapid shutdown.
- Add proportional oversight: require human approval for sensitive actions while allowing lower-risk tasks to remain autonomous.
The secure way to authenticate an autonomous AI agent is not to give the model a powerful secret. Give the deployed agent a distinct workload identity, prove it with a suitable machine-authentication mechanism, and constrain everything it can do through authorization, lifecycle controls, monitoring, and revocation.